“What data do you hold?”
In a workspace
- Order documents you upload and the fields extracted from them.
- Account and workspace records: names, email addresses, roles, settings.
- An audit trail of actions taken in the app.
Axiom OrderFlow / Privacy
A plain-language account of what data Axiom OrderFlow handles, who processes it, and how the public demos work. We would rather be clear than comprehensive-sounding.
Last updated: October 2026Axiom NeurophysiologySecurity overviewTermsRefunds
This is a product prototype policy. It describes what the software does today, and it is pending counsel review before any customer handling protected health information.
Four questions, answered before the document starts.
“What data do you hold?”
“What do you do with it?”
“Who else touches it?”
“What about the demos?”
Axiom OrderFlow is a healthcare operations product from Axiom Neurophysiology (referred to here as Axiom, or we). It helps neurodiagnostics departments intake EEG orders, review extracted fields, and manage the downstream workflow. This policy explains what data we handle and how.
When your organization uses Axiom OrderFlow, we process the order documents you upload and the data extracted from them, plus your account and workspace records (names, email addresses, roles, workspace settings) and an audit trail of actions taken in the app.
This data belongs to your organization. We act as a processor of it on your behalf, under your agreement with us.
Access is scoped to your organization and enforced at the database with row-level security, and that scoping is continuously tested against supported access paths. We do not sell customer data, and we do not use the contents of your order documents to train AI models.
We use strictly necessary cookies to keep you signed in and to operate the app, plus your browser's local storage for small conveniences such as a remembered view or a collapsed panel. We do not run analytics, advertising, or cross-site tracking scripts, so there is nothing to opt in or out of and we do not show a consent banner. If that ever changes, we will ask before setting any non-essential cookie.
We rely on a small set of vendors to run the service. Each is engaged under its own terms.
| Subprocessor | What it does | When it applies |
|---|---|---|
| Supabase | Managed Postgres database, authentication, and file storage. | Always |
| Vercel | Application hosting and serverless compute. | Always |
| Anthropic | AI extraction of fields from uploaded order documents. A human reviews and approves every result. | Optional, by configuration |
| Resend | Transactional and notification email. | Optional, when enabled |
| Sentry | Error monitoring, configured to strip request data and user context before an event is sent. | Optional, when enabled |
| Copies selected tracker columns into a Google Sheet that your administrator connects. | Optional, only if connected | |
| Upstash | Rate-limit counters for the public demo endpoints. | Optional, when enabled |
Before a workspace is authorized for protected health information, the applicable vendor agreements, including Business Associate Agreements where required, are completed alongside a security review. We describe that as the sequence we follow, not as agreements already in place, and we do not claim certifications we do not hold.
The platform is restricted to de-identified or synthetic data. Demo workspaces are for synthetic data only, and that restriction is contractual and operational rather than technical.
A database constraint pins the patient-identifying mode off, but it governs the mode flag, not the contents of a field: this release does not technically prevent someone typing patient information into an order, so please do not enter or upload real PHI.
Do not enter or upload real Protected Health Information into a workspace, a demo, or a demo request until that workspace has been authorized for it.
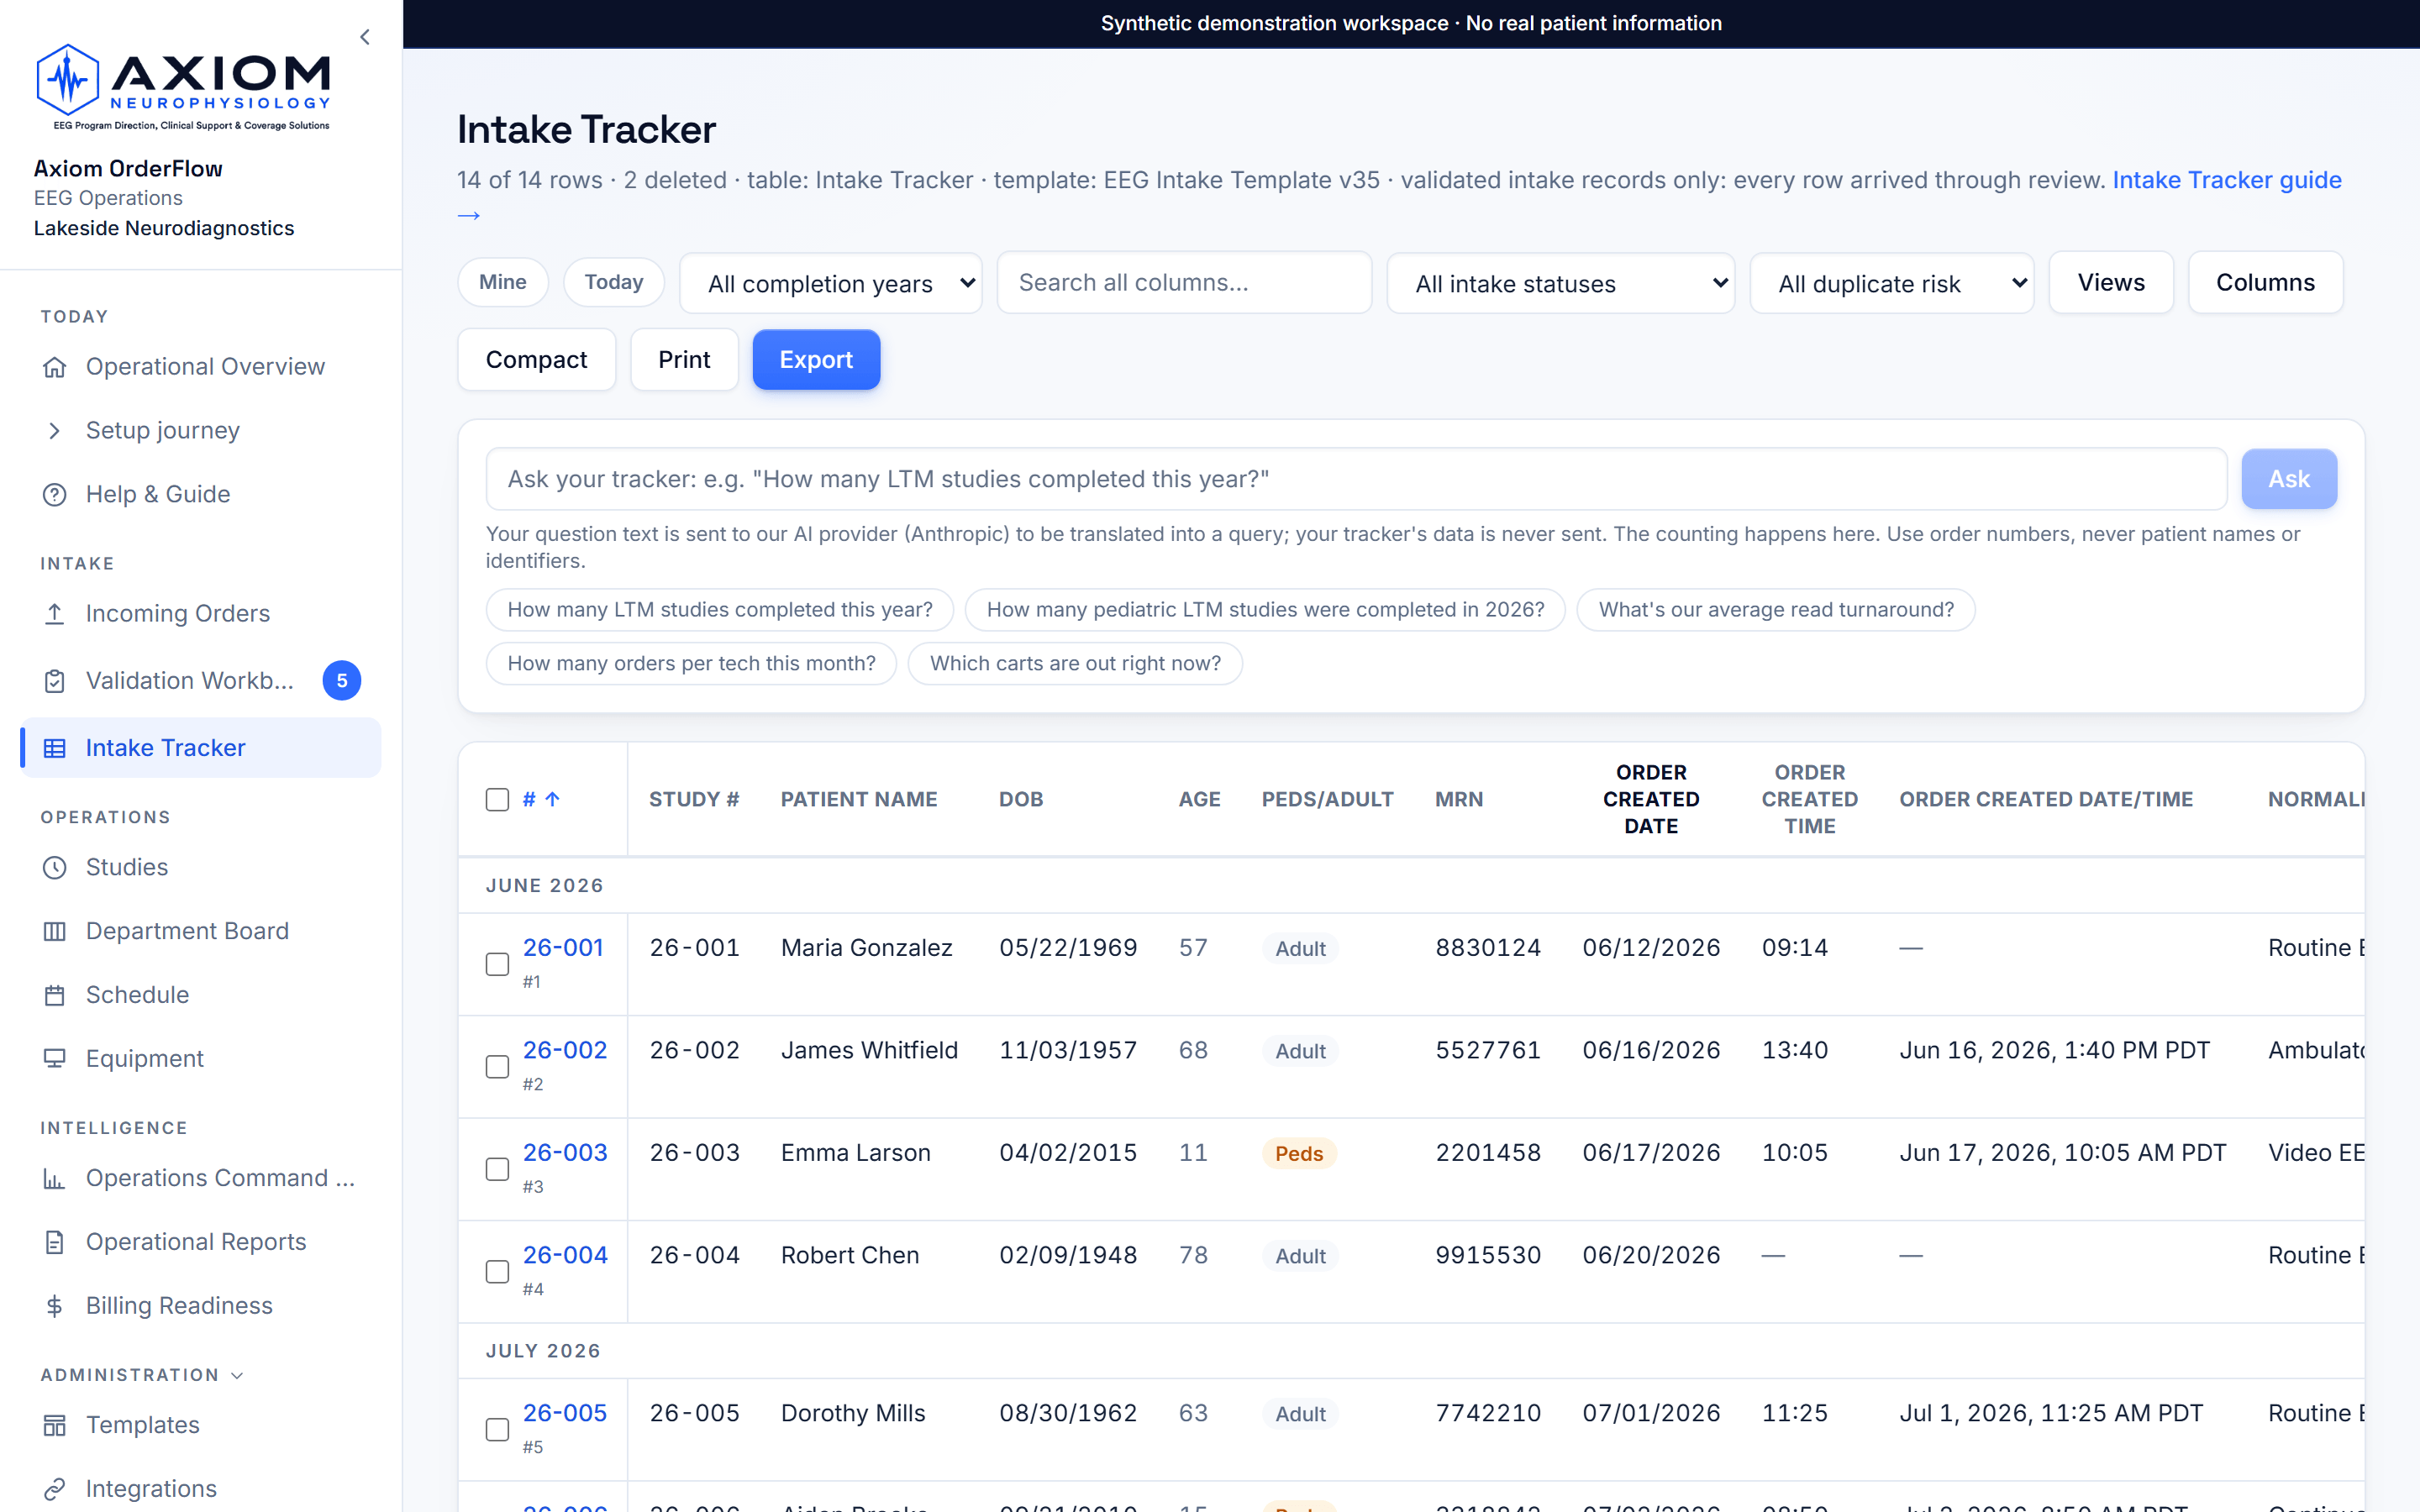
Two of them: a live read-only demo, and a try it with your own order form extraction demo. Both are labeled for synthetic or blank forms only.
Live demo
Try it with your own form
Within a customer workspace, stored order PDFs follow the retention window your administrator configures. Settled orders are swept nightly, and each purge is recorded in the audit trail. The extracted data, tracker rows, and audit history are retained per your agreement.
Disposable demo accounts are deleted automatically. On termination, we return or delete customer data as described in your agreement.
Error monitoring is optional and off unless configured. When it is enabled, it is set to strip request data and user context before an event is transmitted, so a diagnostic report carries the fault and not the record that triggered it.
You can ask for a copy of the personal information we hold about you, ask us to correct it, or ask us to delete it. Email info@axiomeeg.com with the subject line "Data request" from the address your account uses. We confirm receipt within 5 business days and complete the request within 30 days; if we need longer we tell you why.
If the information sits in a customer workspace, that organization controls it, so we pass your request to its administrator and help them complete it. Some records are not erased on request: the audit trail is kept so an organization can show who did what, and an organization may be required to keep clinical or billing records. When that applies we say which records and why, and restrict their use instead.
Details you send through the website demo form are deleted on request.
Axiom OrderFlow is a workplace tool for healthcare staff. It is not directed to children and we do not knowingly collect personal information from anyone under 16. Accounts are created by, or on invitation from, an employer. Orders for pediatric patients are processed on behalf of the healthcare organization that holds them, under its instructions, and are never collected from a child directly. If you believe a child has given us personal information, email info@axiomeeg.com and we will delete it.
If you are a member of a customer workspace, your workspace administrator manages your access and can offboard your account. For requests about data your organization controls, contact your administrator first.
For anything else, including questions about this policy, email info@axiomeeg.com.
We may update this policy as the product changes. The date at the top of this page reflects the current version.
The Security overview covers access controls, audit, and the implementation sequence in more detail. Questions go to info@axiomeeg.com.
An operations review covers the workflow. Your IT, privacy, and security reviewers are welcome in the same conversation.
Or email info@axiomeeg.com